GHSA-4j89-2c4f-44c6 CVE-2026-52796 GO-2026-5124
Gogs has DoS in rendering issue index pattern
- Severity
- 3.5 / 10
- Low · CVSS 3.1
- Exploit chance (EPSS)
- 0.28%
- Chance of exploitation in the next 30 days. Higher than 21.00% of scored vulnerabilities.
- Known exploited
- No
- Not in CISA's catalog
- Weakness
- CWE-1336 Improper Neutralization of Special Elements Used in a Template Engine
- Fix
0.14.3- Upgrade gogs.io/gogs to this version or later
Description
Summary
Special template of issue index pattern may cause panic.
Details
in internal/markup/markup.go
link = fmt.Sprintf(`<a href="%s">%s</a>`, com.Expand(metas["format"], metas), m)
Issue index pattern is rendered to link with com.Expand.
However, com.Expand is not safe.
i = strings.Index(template, "}")
if s, ok := match[template[:i]]; ok {
when { is found but } not found, i comes to 1, template[:-1] will be called, and then panicked
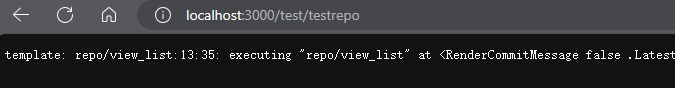
finally, all pages than contains issue index are unavailable.
PoC
- set issue index pattern as follow
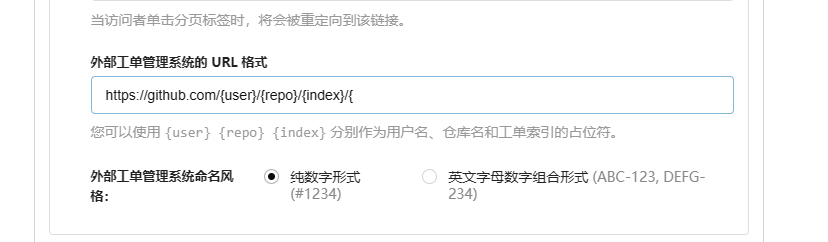
- add a commit which point to an issue in its msg
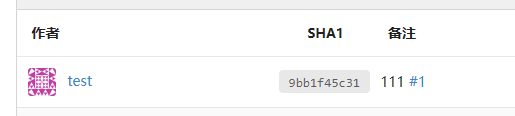
using #1 above
Impact
DoS that cause part of pages of the specify repo unavailable.
Affected versions
Go
| Package | Vulnerable | Fixed in |
|---|---|---|
| gogs.io/gogs | < 0.14.3 |
0.14.3 |
| gogs.io/gogs | all versions |
No fix yet |
How to fix
Move to the fixed version or later with your package manager, update the lockfile, and run your tests. If the package only arrives through another dependency, upgrade that dependency first. If none of its releases pulls a fixed version yet, force the version with your package manager's override.
gogs.io/gogs Go → 0.14.3
- go
go get gogs.io/gogs@v0.14.3 && go mod tidy
Severity breakdown
CVSS 3.1 3.5
CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:N/A:L
- Attack vector
- Network
- Attack complexity
- Low
- Privileges required
- Low
- User interaction
- Required
- Scope
- Unchanged
- Confidentiality
- None
- Integrity
- None
- Availability
- Low
Weakness
CWE-1336: Improper Neutralization of Special Elements Used in a Template Engine
The product uses a template engine to insert or process externally-influenced input, but it does not neutralize or incorrectly neutralizes special elements or syntax that can be interpreted as template expressions or other code directives when processed by the engine.
How to prevent it
- Architecture and Design: Choose a template engine that offers a sandbox or restricted mode, or at least limits the power of any available expressions, function calls, or commands.
- Implementation: Use the template engine's sandbox or restricted mode, if available.
References
Advisories
Packages
Other links
Timeline
- Published
- Last updated by the source
- Latest EPSS score
Related advisories
| Advisory | Severity | Why it's related |
|---|---|---|
| GHSA-mq8m-42gh-wq7r Gogs vulnerable to a bypass of CVE-2024-55947 | High Known exploited | Also affects gogs.io/gogs |
| GHSA-3w28-36p9-w929 Gogs's Unauthenticated Jupyter Notebook (ipynb) Sanitizer allows arbitrary data: URIs leading to XSS | Medium | Also affects gogs.io/gogs |
| GHSA-744x-3838-5r56 Gogs Vulnerable to Unauthenticated Organization Teams Information Disclosure via API | Medium | Also affects gogs.io/gogs |
| GHSA-xp79-5mx3-jx52 Gogs has Unauthenticated Asymmetric Denial of Service (DoS) via SSH Handshake Stall (File Descriptor Exhaustion) | Medium | Also affects gogs.io/gogs |
| GHSA-c39w-43gm-34h5 Gogs has Path Traversal in organization name that results in RCE through Git hooks | Critical | Also affects gogs.io/gogs |
| GHSA-6p9m-q3jp-47h4 Gogs: LFS dedupe path leaks private repo content across tenants | High | Also affects gogs.io/gogs |
| GHSA-89mr-xqfv-758m Gogs: UploadRepoFiles writes outside repo working tree via committed parent sym | Critical | Also affects gogs.io/gogs |
| GHSA-wmfg-5p4h-5fw3 Gogs allows users to write to readonly repositories using receive-pack + service=git-upload-pack confusion | High | Also affects gogs.io/gogs |
MergeHarbor checks every repository's dependencies against this database, ranks what matters by exploitability and reachability, routes it to the owning team and opens the fix pull request.
Check your repos with MergeHarbor