CriticalSecurity
Tenant filter missing on export query
api/handlers/export.go:88
The new export endpoint queries invoices by id only. Every other handler in this package scopes by org_id; this one returns another tenant's data when ids are guessed.
AI code review for engineering organizations
MergeHarbor reviews every pull request with the context of all your repositories, verifies each finding before it is posted, and learns your team's standards. It runs in our cloud or yours, with SSO, audit logs, and predictable cost per review.
Works with the code hosts you already run — in the cloud or self-managed
GitHub
Cloud · Enterprise Server
GitLab
Cloud · Self-Managed
Bitbucket
Cloud · Data Center
Gitea
Self-hosted · Forgejo
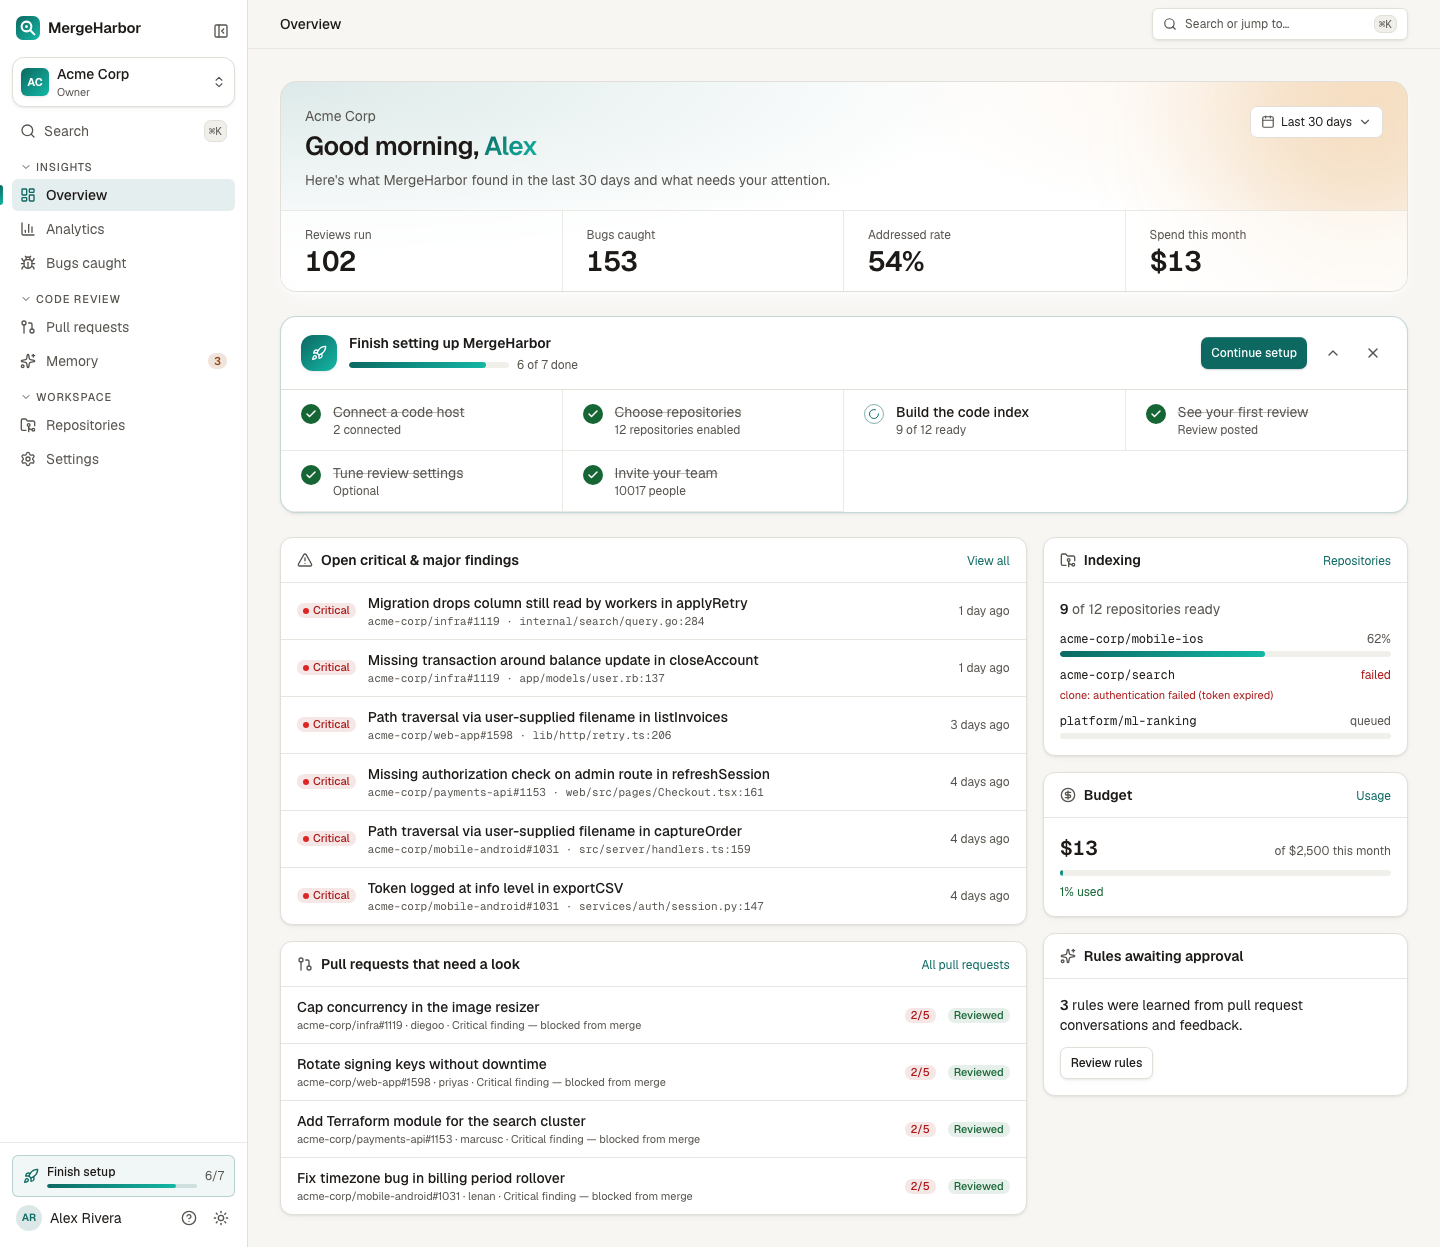
The console
Critical findings, pull requests waiting on a fix, indexing progress, and spend against budget — in one place for every team.
How it works
Diff-only tools comment on the lines that changed. MergeHarbor follows the change through the codebase, then checks its own work.
MergeHarbor builds a graph of every repository — files, symbols, and call relationships — plus a semantic index, and keeps both current with each push.
An agent reads the change, follows callers and callees across the codebase, searches for similar code, and checks history before it forms an opinion.
Every finding goes through an independent verification pass that tries to disprove it. Only findings that survive are posted, with a confidence score.
Rules written in plain English, your existing CLAUDE.md and AGENTS.md files, and the team's reactions to comments shape every later review.
What it catches
Cross-file logic errors, missing authorization, races, and data-integrity problems — reported with the evidence that led to them.
api/handlers/export.go:88
The new export endpoint queries invoices by id only. Every other handler in this package scopes by org_id; this one returns another tenant's data when ids are guessed.
worker/pool.py:141
drain() releases _lock and then writes to _inflight. Two workers draining at once can drop a job. The callers in scheduler.py run drain() concurrently.
billing/ledger.ts:212
updateBalance() is called after tx.commit(). If it fails, the ledger entry exists without the balance change; the retry in capture() then double-credits.
Illustrative findings in the format MergeHarbor posts on pull requests.
Your standards
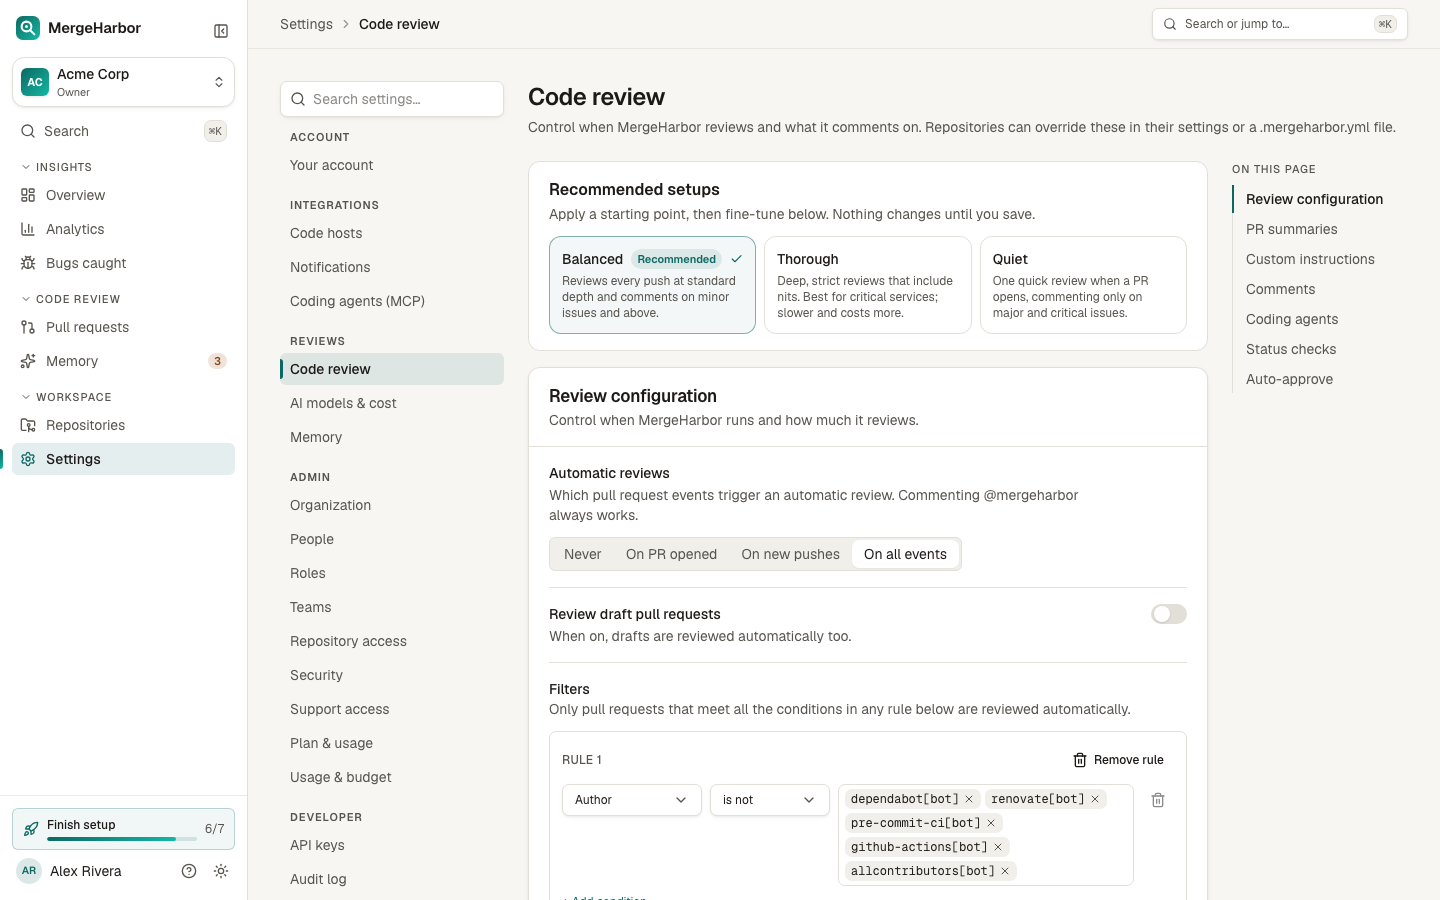
Set strictness, categories, and filters for the organization, override them per repository, and keep repository-specific rules in version control.
Plain-English rules. Teach a rule from the console or in a pull request with @mergeharbor remember, scoped to the paths it applies to.
Context you already wrote. CLAUDE.md, AGENTS.md, Cursor rules, and a knowledge base of design documents are read on every review.
Learning with approval. Patterns in your team's reactions become proposed rules that an admin approves before they take effect.
Tamper-proof configuration. .mergeharbor.yml is read from the merge base, so a pull request cannot change how it is reviewed.
In your workflow
MergeHarbor posts on the pull request and gets out of the way. No new tool to check, no extra step to merge.
@mergeharbor review, or teach a rule without leaving the pull request.
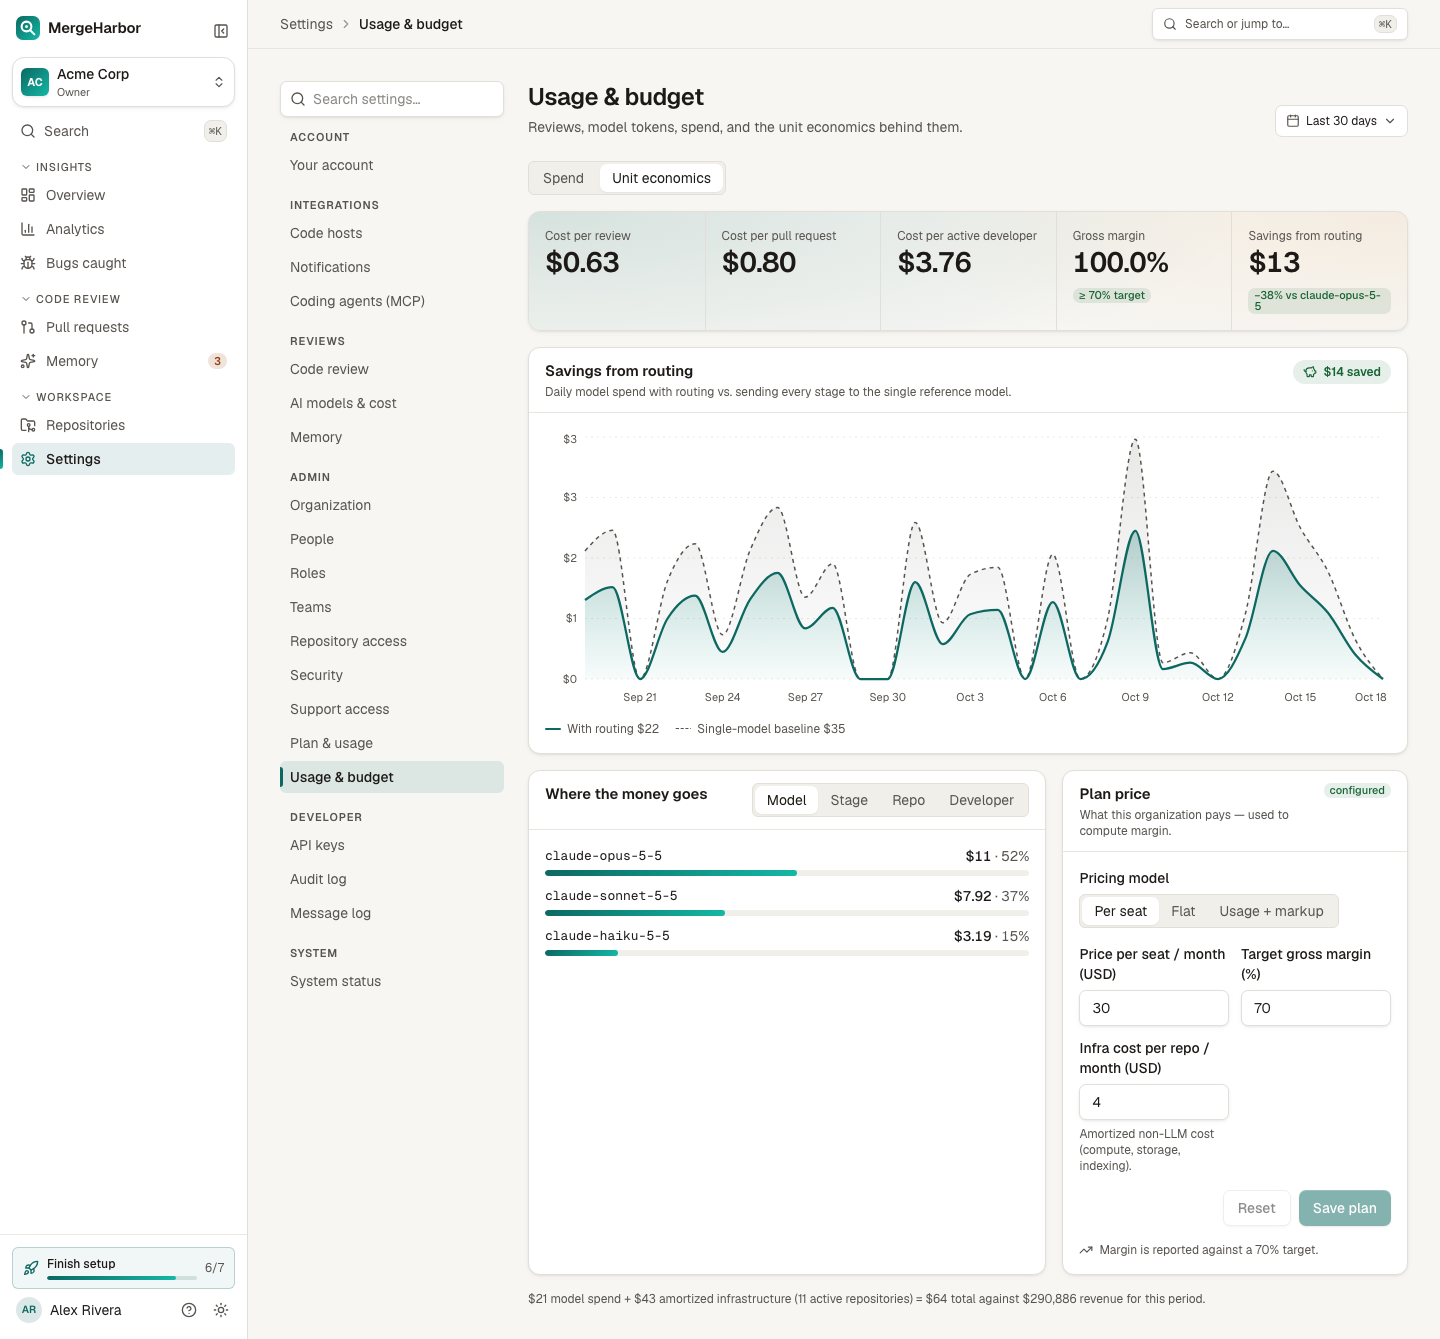
Predictable cost
A documentation change does not need the most expensive model. A change to payments code does. MergeHarbor decides per pull request, and shows you the bill.
Built for enterprises
Run MergeHarbor in your own cloud, connect it to your identity provider, and keep a tamper-evident record of every action.
Design partner program
We work closely with a small group of engineering organizations on deployment, review quality, and the roadmap. Partners get direct access to the engineers building MergeHarbor and preferred pricing.
Linters check rules on individual files, and most AI reviewers only see the lines that changed. MergeHarbor indexes your repositories as a graph of files, symbols, and calls, so the reviewer can trace a change to its callers, compare it with similar code, and read history before reporting. Each finding then passes an independent verification step before it is posted.
GitHub, GitHub Enterprise Server, GitLab (including self-managed), Bitbucket Cloud, Bitbucket Data Center, Azure DevOps Services, Azure DevOps Server (2020 and later), and Gitea or Forgejo. Self-managed hosts on private networks are supported when MergeHarbor is self-hosted or can reach them.
Symbol-level indexing covers Go, Python, JavaScript, TypeScript, Java, Rust, Ruby, C#, C, and C++. Other languages are indexed for search and reviewed with the same agent, with less structural context.
No. Customer code is never used for training, secrets are removed before content reaches a model, and you can choose where inference runs or bring your own model provider accounts.
Yes. MergeHarbor ships as container images with a Helm chart for Kubernetes and Terraform for AWS. Self-hosted deployments support SSO, audit export, and your own model provider accounts.
Connecting a code host and choosing repositories takes a few minutes. Reviews start immediately; indexing runs in the background and adds codebase context as it completes.
Have another question? Talk to our team
Connect a code host in minutes. Reviews start before indexing finishes.